Which clients need certificates?
Which clients need certificates installed? How do we plan for this? What can we do to prepare?
Web-browser-based clients and clients that are distributed via a public third-party application distribution service or store, for example Google Play or Apple AppStore, should not require you to install a certificate. XProtect Mobile will not use installed certificates. XProtect Mobile can only use trusted third-party certificates.
If the XProtect servers (Management Server and Recording Server) are installed on computers that are joined to the Domain, and the users who are logging into the Smart Client are all Domain users, the Domain will handle all public key distribution and authentication required to establish secure communications.
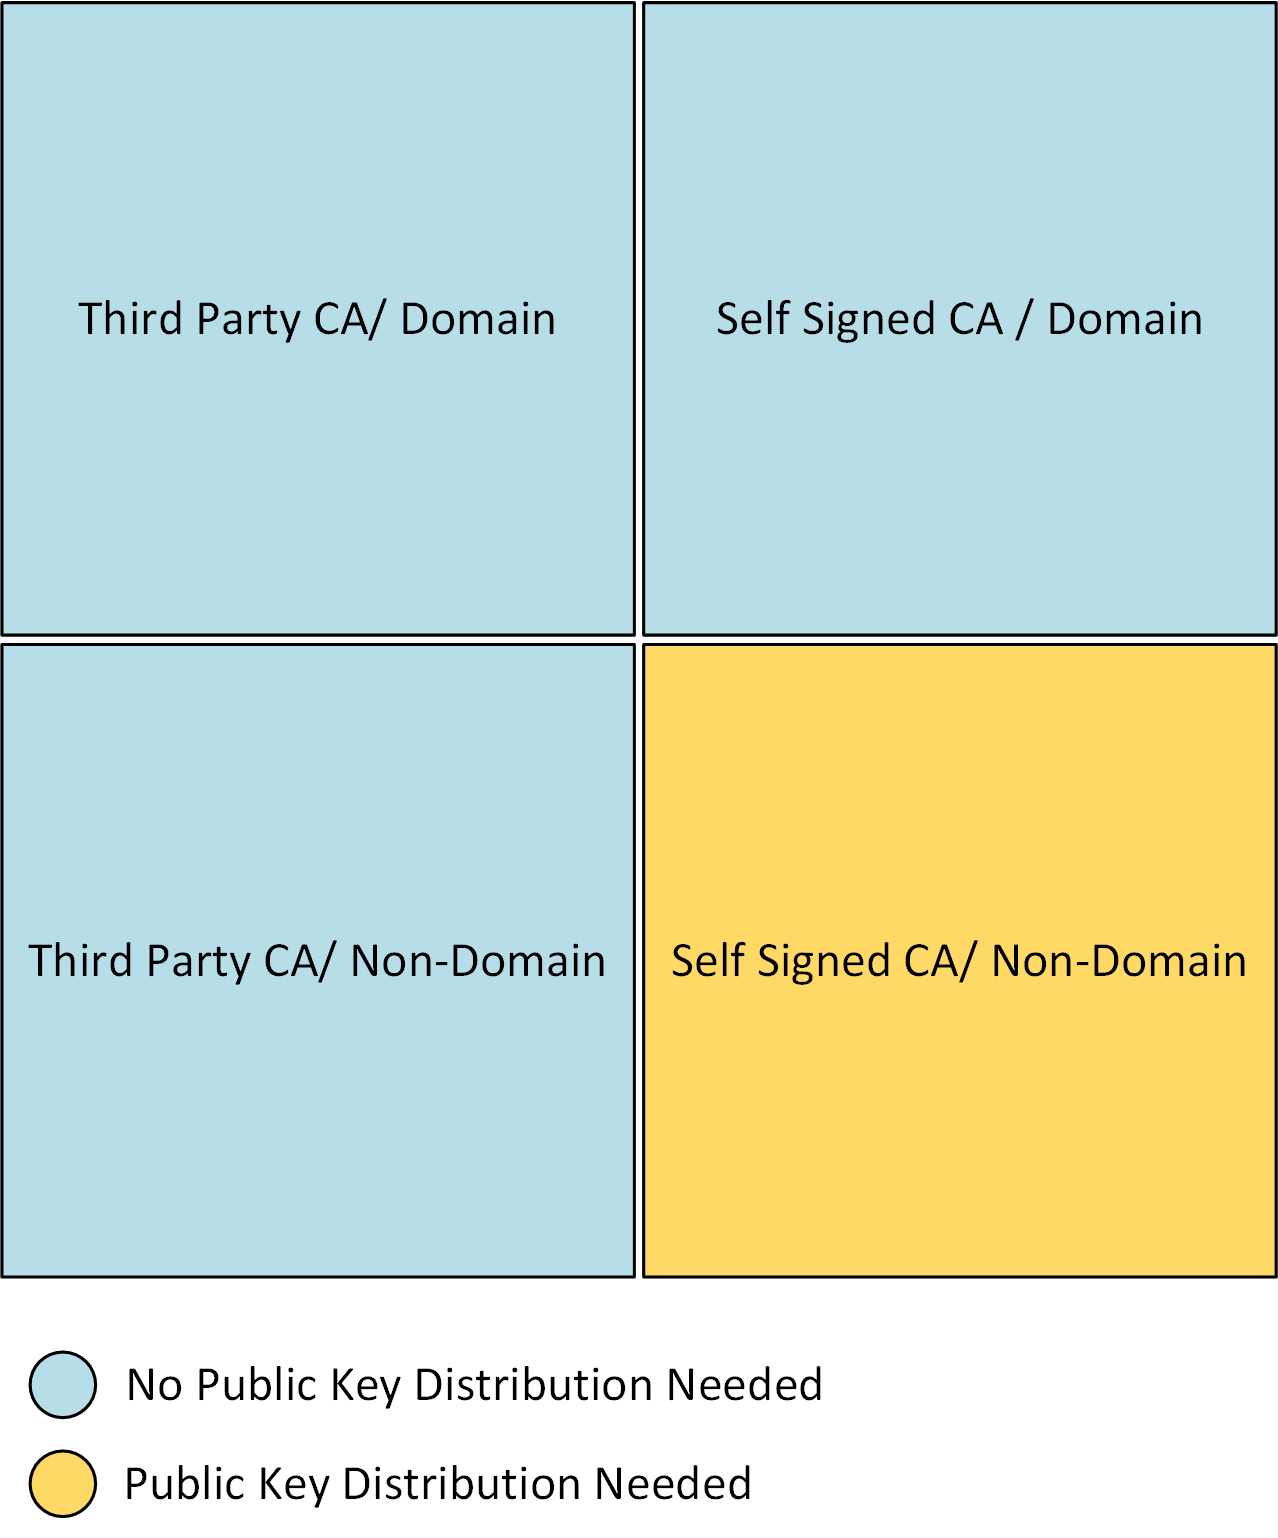
Only in a scenario where Active Directory Certificate Services (AD CS) is used to create self-signed certificates and the resources (users and computers) are operating in a non-domain environment would there be any need to distribute public keys to client workstations.
See also Install certificates on the clients and Import client certificates.