מגדיר כניסה יחידה (SSO)
BriefCam מציע שלוש אפשרויות מוכנות לכניסה יחידה, וממשק ליישום פתרון מותאם אישית לכניסה יחידה.
שלוש אפשרויות SSO המובנות הן:
SSO מבוסס SAML שבו תוכל לאמת ספק אסימון SAML קיים. ראה SSO מבוסס SAML לקבלת מידע אודות אופן הפריסה.
כניסה יחידה ל- Active Directory, שבה אנו מתחברים ל- active directory ומסנכרנים משתמשים וקבוצה משם. לקבלת מידע על אופן הפריסה, עיין שילוב Microsoft Active Directory בסעיף BriefCam מדריך למנהל מערכת.
כניסה יחידה Milestone XProtect. בהתקנות של Milestone אנו מציעים אפשרות להשתמש ב-Milestone Client וב-Directory כדי לספק פתרון של כניסה יחידה.
SSO מבוסס SAML
התכונות ההכרחיות (טענות/מטה-נתונים של SAML) הנדרשות עבור BriefCamSSO מבוסס SAML הן:
דואל
שם פרטי
שם משפחה
UPN
המשתמשים BriefCam שנוצרים באופן אוטומטי במהלך תהליך ה-SSO נוצרים על בסיס תכונת הדוא״ל שהתקבלה בתגובת ה-SAML.
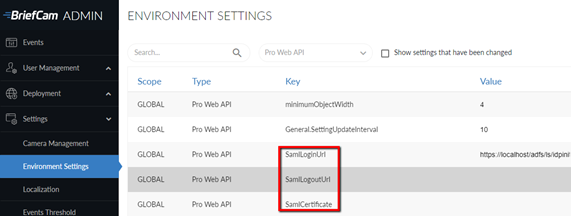
כדי לשלב ספק אסימוני SAML קיים (כגון Microsoft ADFS) עם BriefCam, השתמש BriefCam בתשתית SAML, על ידי הזנת פרטי ספק האסימונים שלך וכתובות URL במקומות המתאימים במקטע ה - Web API של הגדרות הסביבה :
SamlLoginUrl - זוהי נקודת הקצה לכניסה ל- SAML, שהיא ספק אסימוני SAML המגיב לבקשות אימות SAML. בעת הכניסה ל-BriefCam, המשתמש מנותב מחדש לכתובת זו עם פרמטר המורה לנקודת הקצה להחזיר BriefCam את פרטי הכניסה לאחר הכניסה למערכת.
SamlLogoutUrl - זוהי נקודת הקצה של היציאה של SAML, המספקת פונקציונליות של יציאה. המשתמשים ינותבו מחדש לכתובת זו לאחר שיצאו BriefCam.
SamlCertificate - זוהי טביעת האצבע של אישור SAML, שהיא מזהה ייחודי שניתן על-ידי Windows עבור אישור SAML זה. האישור, שאמור להיות מותקן במחשב המקומי, משמש להצפנת התקשורת בין לקוח SAML של BriefCamSAML לספק אסימוני SAML.
דוגמת תגובה
<samlp:Response xmlns:samlp="urn:oasis:names:tc:SAML:2.0:protocol"
xmlns:saml="urn:oasis:names:tc:SAML:2.0:assertion"
ID="_abc123"
Version="2.0"
IssueInstant="2025-01-20T12:00:00Z"
Destination="https://briefcamhost.domain.com/ProWebApi/AuthenticationApi/AuthenticateSaml">
<saml:Issuer>https://idp.example.com</saml:Issuer>
<samlp:Status>
<samlp:StatusCode Value="urn:oasis:names:tc:SAML:2.0:status:Success"/>
</samlp:Status>
<saml:Assertion ID="_def456"
IssueInstant="2025-01-20T12:00:00Z"
Version="2.0">
<saml:Issuer>https://idp.example.com</saml:Issuer>
<saml:Subject>
<saml:NameID Format="urn:oasis:names:tc:SAML:1.1:nameid-format:emailAddress">
user@example.com
</saml:NameID>
<saml:SubjectConfirmation Method="urn:oasis:names:tc:SAML:2.0:cm:bearer">
<saml:SubjectConfirmationData NotOnOrAfter="2025-01-20T13:00:00Z"
Recipient="https://briefcamhost.domain.com/ProWebApi/AuthenticationApi/AuthenticateSaml"/>
</saml:SubjectConfirmation>
</saml:Subject>
<saml:Conditions NotBefore="2025-01-20T12:00:00Z" NotOnOrAfter="2025-01-20T13:00:00Z">
<saml:AudienceRestriction>
<saml:Audience>https://briefcamhost.domain.com/ProWebApi/AuthenticationApi/AuthenticateSaml</saml:Audience>
</saml:AudienceRestriction>
</saml:Conditions>
<saml:AttributeStatement>
<saml:Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress">
<saml:AttributeValue>user@example.com</saml:AttributeValue>
</saml:Attribute>
<saml:Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname">
<saml:AttributeValue>John</saml:AttributeValue>
</saml:Attribute>
<saml:Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname">
<saml:AttributeValue>Doe</saml:AttributeValue>
</saml:Attribute>
<saml:Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/upn">
<saml:AttributeValue>john.doe@example.com</saml:AttributeValue>
</saml:Attribute>
</saml:AttributeStatement>
<saml:AuthnStatement AuthnInstant="2025-01-20T12:00:00Z">
<saml:AuthnContext>
<saml:AuthnContextClassRef>
urn:oasis:names:tc:SAML:2.0:ac:classes:PasswordProtectedTransport
</saml:AuthnContextClassRef>
</saml:AuthnContext>
</saml:AuthnStatement>
</saml:Assertion>
<ds:Signature xmlns:ds="http://www.w3.org/2000/09/xmldsig#">
<ds:SignedInfo>
<ds:CanonicalizationMethod Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#"/>
<ds:SignatureMethod Algorithm="http://www.w3.org/2001/04/xmldsig-more#rsa-sha256"/>
<ds:Reference URI="#_def456">
<ds:Transforms>
<ds:Transform Algorithm="http://www.w3.org/2000/09/xmldsig#enveloped-signature"/>
<ds:Transform Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#"/>
</ds:Transforms>
<ds:DigestMethod Algorithm="http://www.w3.org/2001/04/xmlenc#sha256"/>
<ds:DigestValue>Base64EncodedDigestValue</ds:DigestValue>
</ds:Reference>
</ds:SignedInfo>
<ds:SignatureValue>Base64EncodedSignatureValue</ds:SignatureValue>
</ds:Signature>
</samlp:Response>