Single Sign-On(SSO) 구성
BriefCam Single Sign On을 위한 3가지 맞춤형 옵션과 사용자 지정 Single Sign On 솔루션을 구현하기 위한 인터페이스를 제공합니다.
세 가지 내장 SSO 옵션은 다음과 같습니다.
기존 SAML 토큰 제공자를 인증할 수 있는 SAML 기반 SSO입니다. 이SAML 기반 SSO를 배포하는 방법에 대한 자세한 내용은 을 참조하십시오.
Active Directory Single Sign On을 통해 active directory에 연결하고 거기에서 사용자와 그룹을 동기화합니다. 이 Microsoft Active Directory 통합 배포 방법에 관한 BriefCam 정보는 관리자 안내서의 섹션을 참조하십시오.
Milestone XProtect 싱글 사인온입니다. Milestone 설치에서는 Milestone 클라이언트 및 디렉토리를 사용하여 Single Sign-On 솔루션을 제공하는 옵션을 제공합니다.
SAML 기반 SSO
SAML 기반 SSO에 필요한 필수 속성(SAML BriefCam어설션/메타데이터)은 다음과 같습니다.
이메일
이름
성
UPN
SSO 프로세스 중에 자동으로 생성되는 사용자는 SAML 응답에서 수신한 이메일 속성을 기반으로 생성됩니다BriefCam.
기존 SAML 토큰 제공자(예: Microsoft ADFS)를 BriefCam와 통합하려면BriefCam, 환경 설정의 Pro Web API 섹션에서 적절한 위치에 자체 토큰 제공자의 정보와 URL을 입력하여 SAML 인프라를 사용합니다.
SamlLoginUrl - SAML 인증 요청에 응답하는 SAML 토큰 제공자인 SAML 로그인 엔드포인트입니다. 로그인할 때, 로그인 BriefCam후 엔드포인트에 로그인 정보를 반환하도록 알리는 매개변수와 함께 사용자가 이 주소로 BriefCam 다시 라우팅됩니다.
SamlLogoutUrl - 로그아웃 기능을 제공하는 SAML 로그아웃 엔드포인트입니다. 로그아웃하면 이 주소로 리디렉션됩니다BriefCam.
SamlCertificate - 이 SAML 인증서는 Windows에서 이 SAML 인증서에 대해 부여한 고유 식별자인 SAML 인증서 지문입니다. 로컬 PC에 설치되어야 하는 인증서는 SAML 클라이언트와 SAML 토큰 공급자 간BriefCam의 통신을 암호화하는 데 사용됩니다.
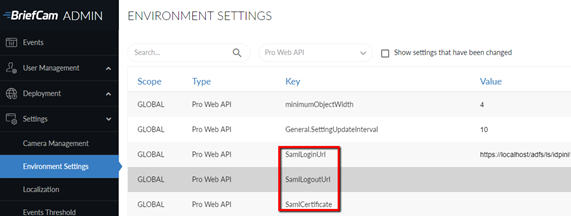
또한 SAML - BriefCam 요구 사항에 대한 ADFS 신뢰 당사자 설정를 참조하십시오.
샘플 응답 예시
<samlp:Response xmlns:samlp="urn:oasis:names:tc:SAML:2.0:protocol"
xmlns:saml="urn:oasis:names:tc:SAML:2.0:assertion"
ID="_abc123"
Version="2.0"
IssueInstant="2025-01-20T12:00:00Z"
Destination="https://briefcamhost.domain.com/ProWebApi/AuthenticationApi/AuthenticateSaml">
<saml:Issuer>https://idp.example.com</saml:Issuer>
<samlp:Status>
<samlp:StatusCode Value="urn:oasis:names:tc:SAML:2.0:status:Success"/>
</samlp:Status>
<saml:Assertion ID="_def456"
IssueInstant="2025-01-20T12:00:00Z"
Version="2.0">
<saml:Issuer>https://idp.example.com</saml:Issuer>
<saml:Subject>
<saml:NameID Format="urn:oasis:names:tc:SAML:1.1:nameid-format:emailAddress">
user@example.com
</saml:NameID>
<saml:SubjectConfirmation Method="urn:oasis:names:tc:SAML:2.0:cm:bearer">
<saml:SubjectConfirmationData NotOnOrAfter="2025-01-20T13:00:00Z"
Recipient="https://briefcamhost.domain.com/ProWebApi/AuthenticationApi/AuthenticateSaml"/>
</saml:SubjectConfirmation>
</saml:Subject>
<saml:Conditions NotBefore="2025-01-20T12:00:00Z" NotOnOrAfter="2025-01-20T13:00:00Z">
<saml:AudienceRestriction>
<saml:Audience>https://briefcamhost.domain.com/ProWebApi/AuthenticationApi/AuthenticateSaml</saml:Audience>
</saml:AudienceRestriction>
</saml:Conditions>
<saml:AttributeStatement>
<saml:Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress">
<saml:AttributeValue>user@example.com</saml:AttributeValue>
</saml:Attribute>
<saml:Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname">
<saml:AttributeValue>John</saml:AttributeValue>
</saml:Attribute>
<saml:Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname">
<saml:AttributeValue>Doe</saml:AttributeValue>
</saml:Attribute>
<saml:Attribute Name="http://schemas.xmlsoap.org/ws/2005/05/identity/claims/upn">
<saml:AttributeValue>john.doe@example.com</saml:AttributeValue>
</saml:Attribute>
</saml:AttributeStatement>
<saml:AuthnStatement AuthnInstant="2025-01-20T12:00:00Z">
<saml:AuthnContext>
<saml:AuthnContextClassRef>
urn:oasis:names:tc:SAML:2.0:ac:classes:PasswordProtectedTransport
</saml:AuthnContextClassRef>
</saml:AuthnContext>
</saml:AuthnStatement>
</saml:Assertion>
<ds:Signature xmlns:ds="http://www.w3.org/2000/09/xmldsig#">
<ds:SignedInfo>
<ds:CanonicalizationMethod Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#"/>
<ds:SignatureMethod Algorithm="http://www.w3.org/2001/04/xmldsig-more#rsa-sha256"/>
<ds:Reference URI="#_def456">
<ds:Transforms>
<ds:Transform Algorithm="http://www.w3.org/2000/09/xmldsig#enveloped-signature"/>
<ds:Transform Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#"/>
</ds:Transforms>
<ds:DigestMethod Algorithm="http://www.w3.org/2001/04/xmlenc#sha256"/>
<ds:DigestValue>Base64EncodedDigestValue</ds:DigestValue>
</ds:Reference>
</ds:SignedInfo>
<ds:SignatureValue>Base64EncodedSignatureValue</ds:SignatureValue>
</ds:Signature>
</samlp:Response>